Configuración de la manipulación de los path attributes que dirigen el best-path. Todos siguen el mismo patrón: una ACL o prefix-list selecciona los prefijos, un route-map hace match y aplica el set, y el route-map se asocia al vecino en la dirección correspondiente. Tras cualquier cambio de política hay que refrescar la sesión (preferir soft reset).
El patrón común
- ACL o prefix-list → selecciona qué prefijos.
- route-map →
matchde esa lista +setdel atributo. neighbor <ip> route-map <nombre> {in | out}→ aplica al vecino.- Refrescar con
clear ip bgp <ip> softpara que la política aplique.
La dirección (in/out) depende del atributo: Weight y Local Preference suelen aplicarse in (afectan tu decisión de salida según lo que aprendes); AS-PATH Prepend y MED suelen aplicarse out (influyen cómo otros te envían tráfico).
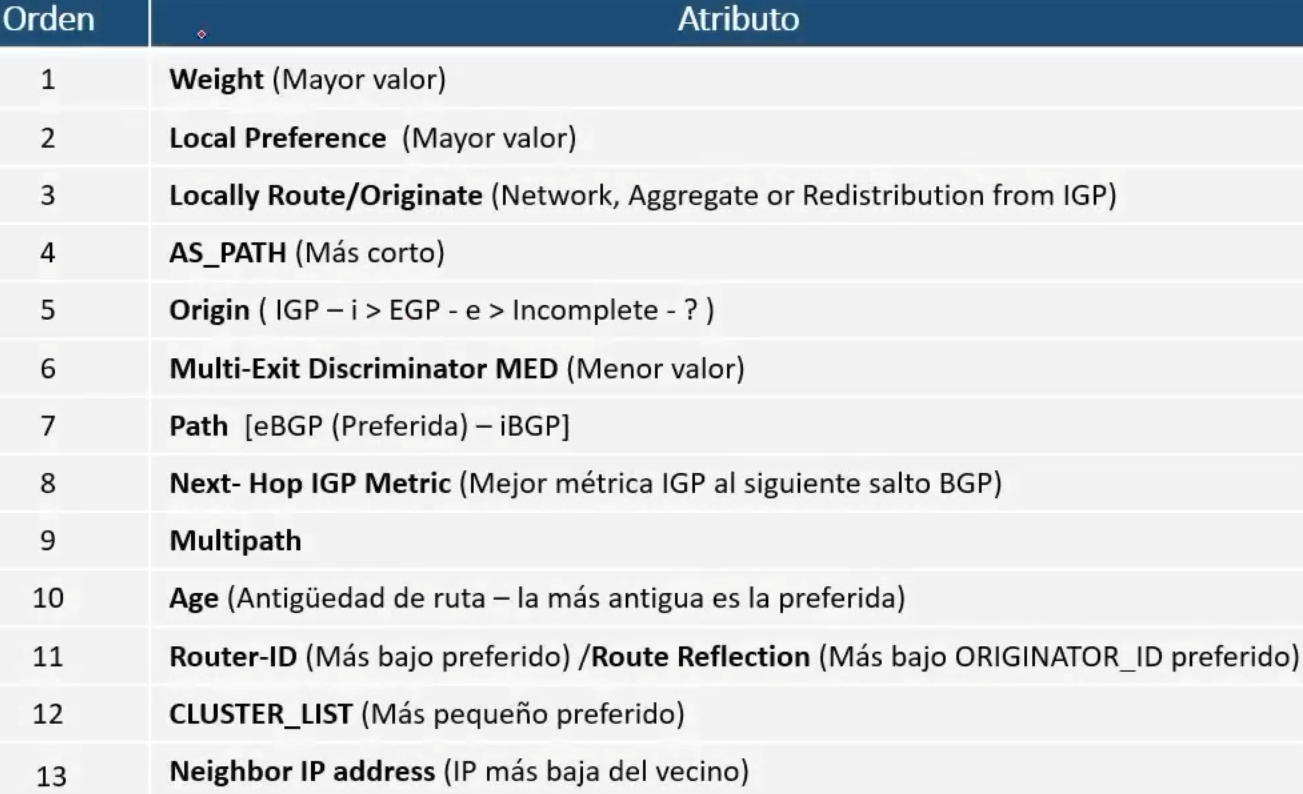
Orden de seleccion de atributo en Path Attributes
1. Weight
El valor tiene significado Local al router solamente.
mayor valor gana, Rango = 0–65535.
Valor por defecto de 0 cuando se recibe de vecino. / Valor por defecto de 32768 cuando se genera la ruta localmente.
No se propaga a los vecinos.
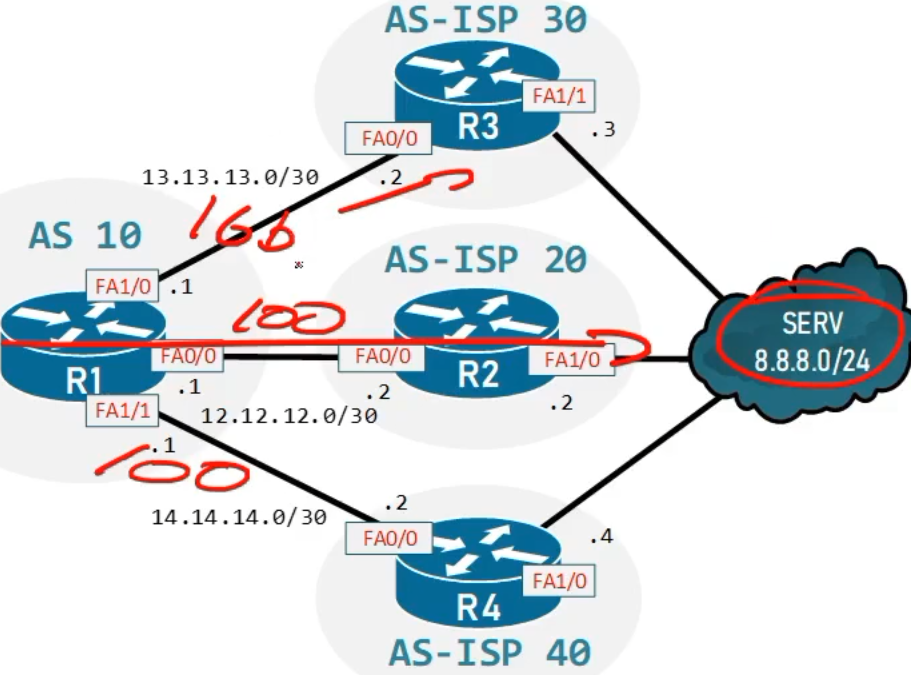
Método granular (route-map, por prefijo)
- Comandos:
R1(config)# access-list 1 permit <ipv4-red-destino> <wildcard>
R1(config)# route-map <name> permit <seq>
R1(config-route-map)# match ip address <acl-name(Asociar)>
R1(config-route-map)# set weight <valor>

R1(config)#router bgp <as-local>
R1(config-router)# neighbor <ipv4-peer> route-map SET_WEIGHT in
- Ejemplo: (Resultado: Se eligio el camino por R3 para llegar a Server 8.8.8.0/24)
R1(config)# access-list 1 permit 8.8.8.0 0.0.0.255
R1(config)# route-map SET_WEIGHT permit 10
R1(config-route-map)# match ip address 1
R1(config-route-map)# set weight 200
R1(config-route-map)# exit
R1(config)# route-map WEIGHT permit 20

R1(config)#router bgp 10
R1(config-router)# neighbor 13.13.13.2 route-map SET_WEIGHT in
Configurar un
Permit any, de no hacerlo hay unimplicit deny. Solucion:R1(config)# route-map WEIGHT permit 20
Una vez configurado hay que reinciar el proceso BGP.
Verificar: Show ip bgp
Método masivo (todos los prefijos de un vecino)
- Comando:
R1(config-router)# neighbor <ip-peer> weight <valor> - Ejemplo:
R1(config-router)# neighbor 14.14.14.2 weight 800= Resultado: Se eligio el camino por R4 a Server.
R1(config)#router bgp 10
R1(config-router)# neighbor 14.14.14.2 weight 800
Aplica el mismo weight a todos los prefijos recibidos de ese vecino.
Local Preference
Permite influenciar la ruta de salida de todo un AS.
Se propaga por iBGP (no a eBGP).
Valor por default 100 / rango 0–4294967295.
Mayor valor gana.
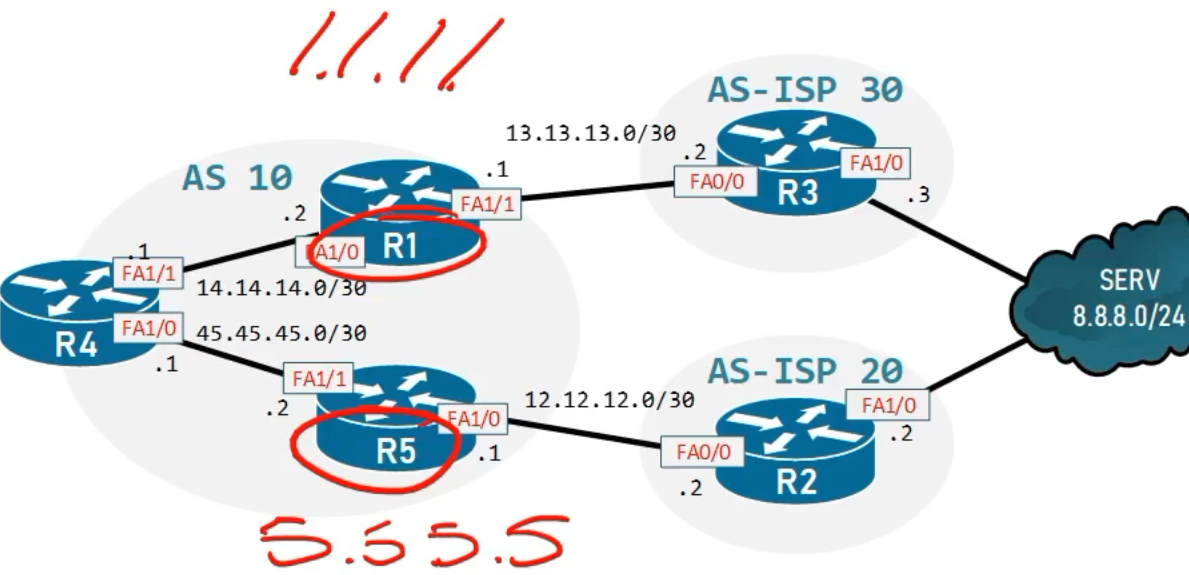
- Problema: Tenemos 2 routers (Border) en un AS, vamos a decidir que ruta (Router) van a usar para salir al servidor.
(La configuracion en R1 o R5 debido a que son los puntos de salida del AS) - Mejora en comparacion a Weight: Si tenemos 10 Routers, es mejor utilizar L.P debido a que en Weight habria que configurarlo 10 veces.
Método granular (route-map)
- Comando:
R1(config)# access-list 1 permit <ipv4-red-destino> <wildcard>
R5(config)# route-map SET_LOCALPREF permit <seq>
R5(config-route-map)# match ip address <acl-name(Asociar)>
R5(config-route-map)# set local-preference <valor>

R5(config)#router bgp <as-local>
R5(config-router)# neighbor <ip-peer> route-map SET_LOCALPREF in
- Ejemplo: (Se escogio el camino por R5 para llegar al Server 8.8.8.0/24)
R5(config)# access-list 1 permit 8.8.8.0 0.0.0.255
R5(config)# route-map LOCALPREF permit 10
R5(config-route-map)# match ip address 1
R5(config-route-map)# set local-preference 200
R5(config-route-map)# exit
R5(config)#route-map LOCALPREF permit 20 = Permit Any

R5(config)#router bgp 10
R5(config-router)# neighbor 12.12.12.2 route-map LOCALPREF in
Una vez configurado hay que reinciar el proceso BGP.
Método global (cambia el default del router)
- Comando:
R1(config-router)# bgp default local-preference <valor> - Ejemplo:
R1(config-router)# bgp default local-preference 800
Situacion: Se escogio el camino por R5 para llegar al Server 8.8.8.0/24.
R1(config)#router bgp 10
R1(config-router)# bgp default local-preference 800
Se aplica en los border routers (puntos de salida del AS); como se propaga por iBGP, todos los routers internos aprenden la salida preferida.
AS-PATH Prepend
Alarga artificialmente el AS-PATH para hacer un camino menos preferido. (Anade AS a la ruta artificialmente.)
Influye tráfico entrante.
La ruta con menor numero de AS sera la elegida en AS-PATH. (No importa el numero de AS-Path, sino los saltos.)
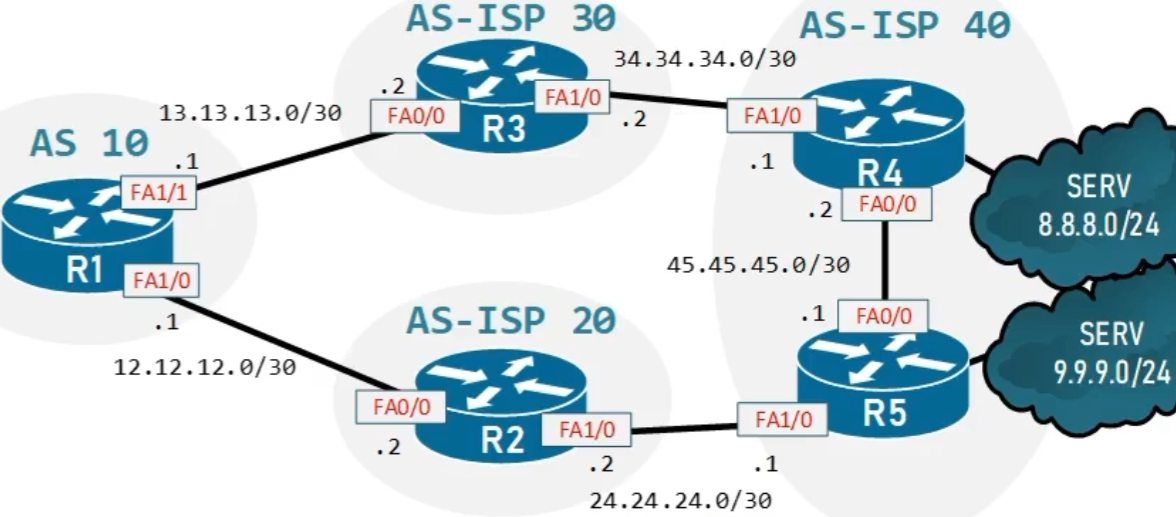
Idea: Hacer balanceo de carga entre dos caminos posibles al destino. Desde R1 quiero acceder a 8.8.8.0/24 mediante R3, Para llegar a la red 9.9.9.0/24 lo haremos por R2.
Solucion: En R5 se le dira a R1 que para llegar a la red 8.8.8.0/24 tienen que atravesar artificialmente 40 AS (x3).
- Comandos:
R1(config)# ip prefix-list <name> seq 10 permit <red-destino>
R1(config)# route-map <name> permit <seq>
R1(config-route-map)# match ip address prefix-list <acl-name>
R1(config-route-map)# set as-path prepend <as-number-propio>
R1(config-router)# neighbor <ip-peer> route-map SET_PREPEND out
- Ejemplo:
R5(config)# ip prefix-list PF seq 10 permit 8.8.8.0/24
R5(config)# route-map ASPATH permit 10
R5(config-route-map)# match ip address prefix-list PF
R5(config-route-map)# set as-path prepend 40 40
R5(config-route-map)# exit

R5(config)# route-map ASPATH permit 20
R5(config-route-map)# exit

R5(config)#router bgp 40
R5(config-router)# neighbor 24.24.24.2 route-map ASPATH out
La decision de salida siempre sera
OUT.
Set as-path prepend= El valor colocado aqui tiene que ser el mismo numero de AS en cual tiene el dispositivo, (AS 40), si se utiliza otro numero pasara un error de enrutamiento.
24.24.24.2= Router vecino de salida.
Prepend siempre con tu propio ASN
Usar un ASN ajeno puede causar que otros AS descarten la ruta por loop prevention o inyectar información de routing falsa. Repite tu propio ASN tantas veces como saltos quieras simular.
- Verificar:
Show ip bgp
MED (Metrica)
Menor valor gana, influye tráfico entrante desde un AS directamente conectado,
Los atributos de MED solo se comparten entre AS directamente conectados.
El valor de MED es enviado solo a los routers de un AS vecino y ese valor es propagado a todos los routers de ese AS. Cuando el AS envia el prefijo a otro AS, el valor de MED es eliminado.
Cuando un router recibe un valor de MED inexistente, y tiene que enviart ese valor a sus iBGP, introduce un valor de MED de 0
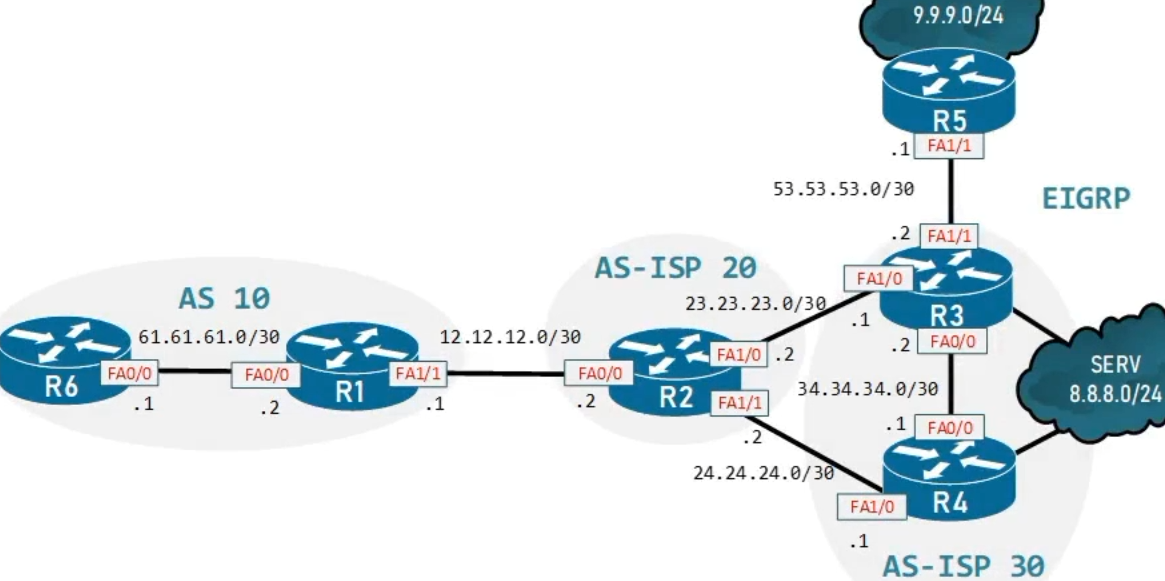
R6 debido a que es iBGP: En el comando show ip bgp vera la conexion hacia 9.9.9.0/24 con una metrica de 0 (Regla de MED.)
Idea: Decirle a los Routers con que interface accedan a nuestro AS (En caso de tener 2 routers en un AS.) Le decimos a nuestro AS vecino por donde conectarse a nuestro AS.
- Comandos:
R1(config)# access-list <number> permit <ipv4-red> <wildcard>
R1(config)# route-map <name> permit <seq>
R1(config-route-map)# match ip address <acl-name>
R1(config-route-map)# set metric <valor>
R1(config-router)# neighbor <ipv4-peer> route-map SET_MED out
Se configura
out.
- Ejemplo: (R3 le daremos un valor de MED 100 a la red 8.8.8.0/24 que va dirigido a R2.)
R3(config)#router bgp 30
R3(config-router)# network 9.9.9.0 mask 255.255.255.0

R3(config)# access-list 1 permit 8.8.8.0 0.0.0.255
R3(config)# route-map MED permit 10
R3(config-route-map)# match ip address 1
R3(config-route-map)# set metric 100

R3(config)# route-map MED permit 20 = Permit Any

R3(config)#router bgp 30
R3(config-router)# neighbor 23.23.23.2 route-map MED out
23.23.23.2= Router vecino de salida.
Communities
Etiqueta rutas para aplicar política a un grupo. Optional transitive. No se envían por defecto.
Set de community en un route-map
R1(config)# ip prefix-list PL_COMM seq 10 permit <red>/<longitud>
R1(config)# route-map SET_COMM permit 10
R1(config-route-map)# match ip address prefix-list PL_COMM
R1(config-route-map)# set community <AS:valor>
R1(config-router)# neighbor <ip-peer> route-map SET_COMM out
Habilita el envío del atributo community (obligatorio)
R1(config-router)# neighbor <ip-peer> send-community
Actuar sobre una community recibida (community-list + route-map)
R1(config)# ip community-list standard CL_1 permit <AS:valor>
R1(config)# route-map MATCH_COMM permit 10
R1(config-route-map)# match community CL_1
R1(config-route-map)# set local-preference <valor>
R1(config-router)# neighbor <ip-peer> route-map MATCH_COMM in
Communities no se envían por defecto
Un error común es hacer
set communityy esperar que el vecino la vea. Cisco no anuncia el atributo community a un peer a menos que se configureneighbor <ip> send-community.
Refrescar tras el cambio
Toda modificación de política requiere refrescar la sesión. Preferir el soft reset para no tumbarla:
R1# clear ip bgp <ip-peer> soft in
R1# clear ip bgp <ip-peer> soft out
Verificación
- Ver el valor de los atributos en la tabla (Weight, LocPrf, Metric/MED, Path):
R1# show ip bgp
Las columnas muestran Weight, LocPrf (Local Preference) y Metric (MED). El AS-PATH prependeado se ve alargado en la columna Path.
- Ver el detalle de atributos de un prefijo, incluyendo communities:
R1# show ip bgp <prefijo>
Muestra Local Preference, MED, AS-PATH completo y las communities asociadas (si send-community está activo en el emisor).
- Ver rutas por community:
R1# show ip bgp community <AS:valor>